Microsoft Copilot Security Risks for Business Leaders
Published:
The biggest Copilot risk is not that it invents sensitive data. It is that it can surface information users were already allowed to access because permissions, sharing, and governance were never cleaned up first.
That is why Copilot readiness is usually a Microsoft 365 governance question before it becomes an AI productivity question.
Microsoft documents that Microsoft 365 Copilot only accesses data that the signed-in user is already authorized to access. NIST’s July 2024 Generative AI Profile also identifies 12 risk categories unique to or intensified by generative AI, including confabulation and data-privacy risk. Those two sources support the same executive point: AI tools often amplify pre-existing governance and permissions problems rather than replacing the need to fix them.
What Copilot changes
Copilot makes existing information easier to find, summarize, connect, and reuse.
That can be valuable. It can also expose long-ignored problems in:
- broad group memberships
- overshared SharePoint and Teams content
- poorly governed guest access
- weak data-classification practices
- inconsistent ownership of sensitive information
In other words, Copilot often reveals old permission problems faster than most organizations expect.
That is why the conversation feels different from ordinary Microsoft 365 administration. A file that was technically accessible but practically hard to find can become much easier to locate, summarize, or reference when AI is layered on top. The risk is not created out of nowhere. It is accelerated by a tool that reduces the friction between access and discovery.
Why the risk feels different
Many businesses have relied on a kind of practical obscurity. Information existed, but it was hard to locate unless someone knew where to look.
Copilot changes that dynamic. If access already exists, discovery becomes easier. That is why oversharing, inherited permissions, and governance drift become more consequential once AI is layered on top.
Leadership should care because the resulting problem is rarely just technical. It can affect confidentiality, client trust, internal data boundaries, HR sensitivity, board materials, and the business’s general ability to explain who should have seen what. That makes Copilot readiness a governance issue before it becomes a productivity program.
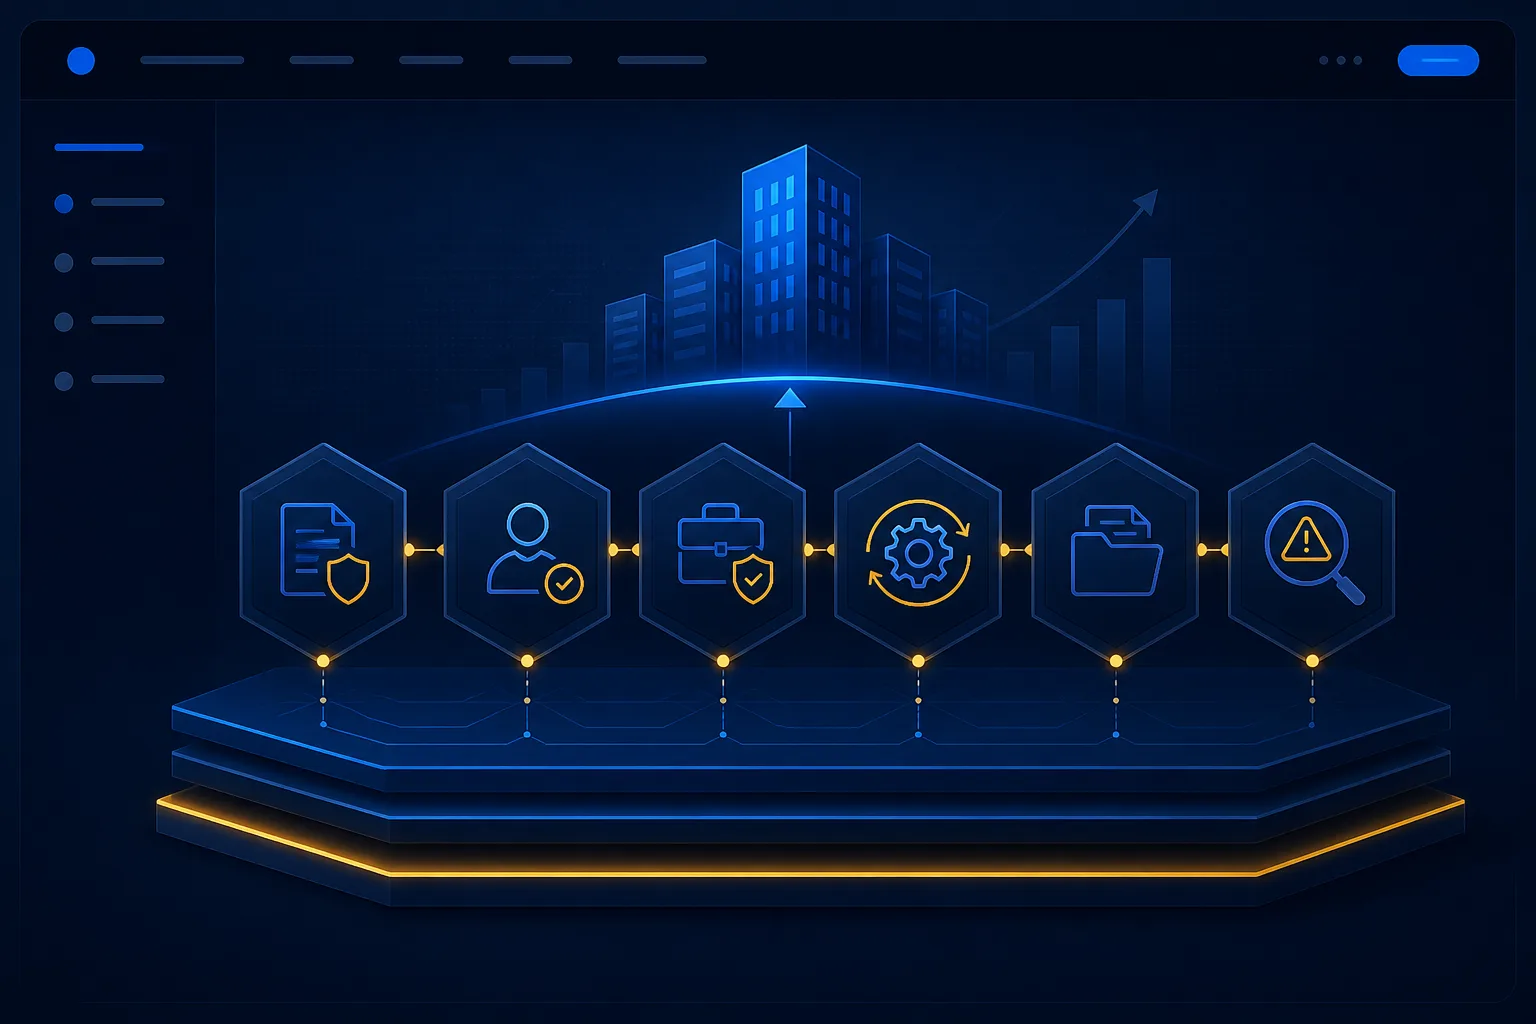
Which organizations are most exposed
Risk tends to be higher in environments with:
- years of uncontrolled sharing growth
- inconsistent file ownership and permissions hygiene
- weak data classification or retention discipline
- too many admins or broad access groups
- limited review of external users and app integrations
- pressure to move quickly on AI without prior access cleanup
Consider a generic professional-services firm where years of Teams sites, shared folders, and broad Microsoft 365 groups have accumulated without consistent ownership. Before AI, those issues may have remained mostly invisible because finding the wrong document still took effort. After AI, weak permissions hygiene becomes much easier to feel operationally. That is the kind of readiness gap executives should want surfaced before rollout, not after.
What should be reviewed first
Before a broad rollout, organizations should examine:
- SharePoint, Teams, and OneDrive permissions hygiene
- sensitivity labels and DLP maturity
- guest access and external collaboration controls
- privileged roles and admin account protection
- data ownership and high-risk content locations
- user guidance for AI-assisted handling of sensitive information
The best starting point is usually not “how fast can we enable Copilot?” but “what would Copilot reveal about the way our environment is already governed?” That shift changes the rollout from a feature decision into a risk-visibility exercise.
What good Copilot readiness looks like
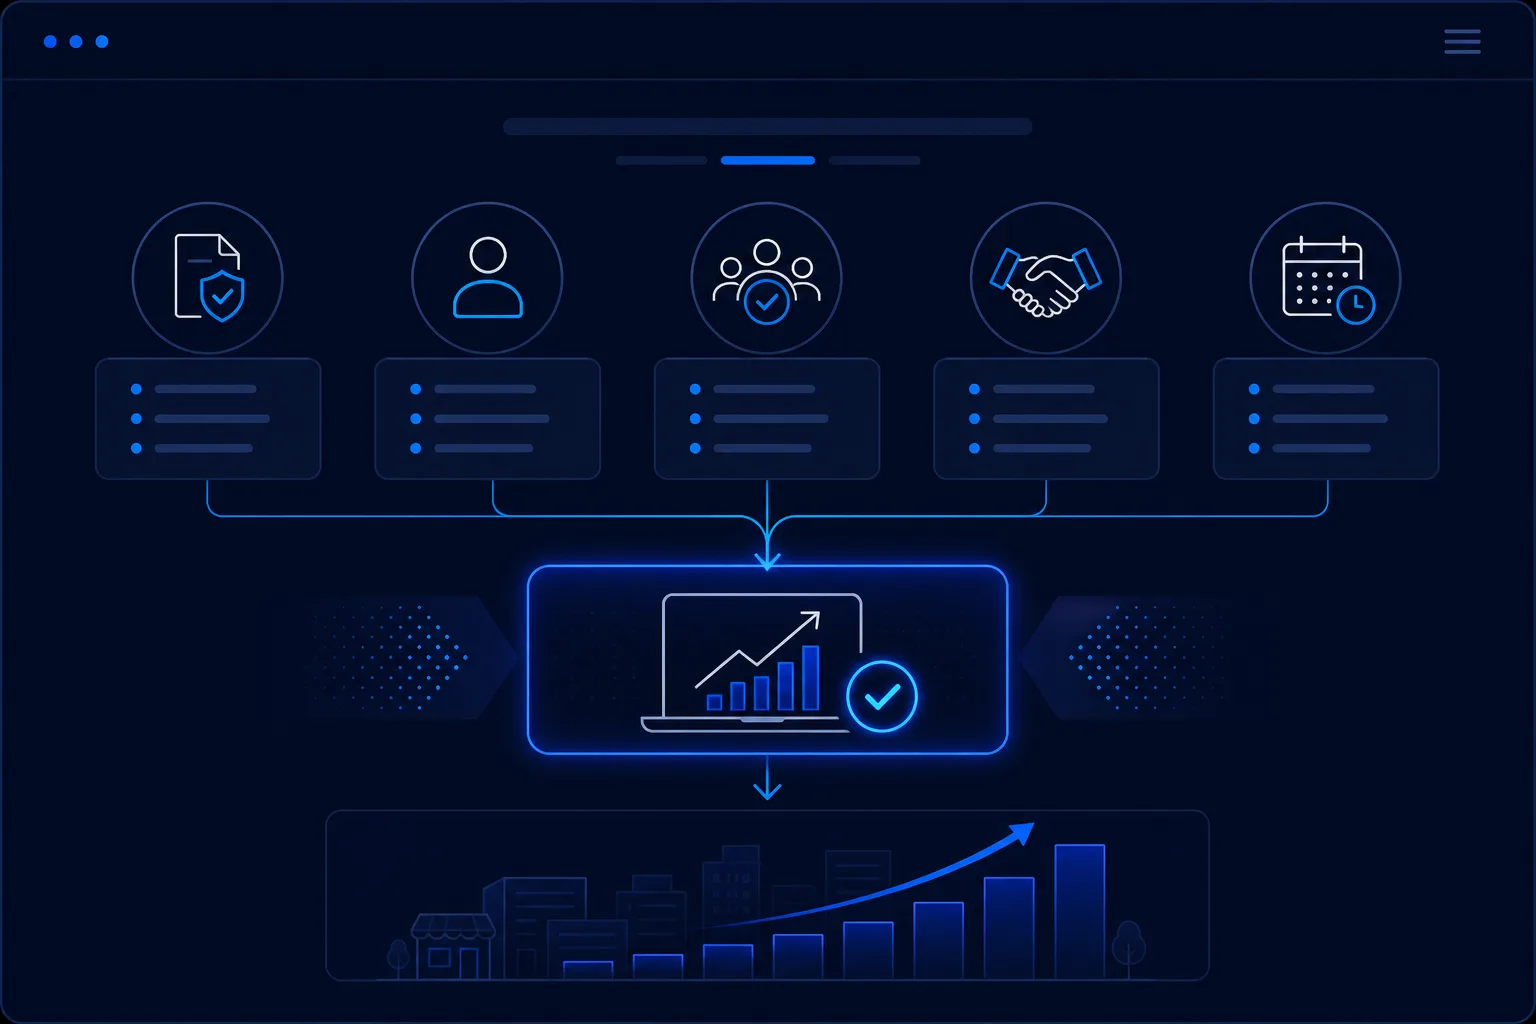
Good readiness does not mean eliminating every risk. It means the business can explain how sensitive data is governed, how permissions are reviewed, who owns high-risk repositories, and how staff should handle AI-assisted discovery of important information.
Poor readiness usually looks like broad access groups, weak classification, unclear ownership, or the assumption that AI can be deployed safely because the environment has “worked fine so far.” That assumption is exactly what a stronger assessment should challenge.
What current evidence says
Microsoft documents that Microsoft 365 Copilot only accesses data that the signed-in user is already authorized to access.
That matters because Copilot risk often reflects existing permissions hygiene rather than a completely new access model.
NIST’s July 2024 Generative AI Profile identifies 12 risk categories unique to or intensified by generative AI, including confabulation and data privacy.
That supports the broader point that AI adoption introduces or amplifies governance and information-handling questions leadership should address explicitly.
The evidence helps clarify the issue: Copilot does not remove the need for governance. It raises the cost of weak governance by making existing access more powerful and easier to operationalize.
Frequently asked questions
Final takeaway
Copilot does not create most access problems. It accelerates the visibility and usefulness of permissions that may already be too loose.
Assess Microsoft 365 governance before a broad Copilot rollout.
Before you roll out Copilot broadly, assess whether your Microsoft 365 environment is governed well enough to support it safely.