Risk Assessment vs Compliance Audit
Published:
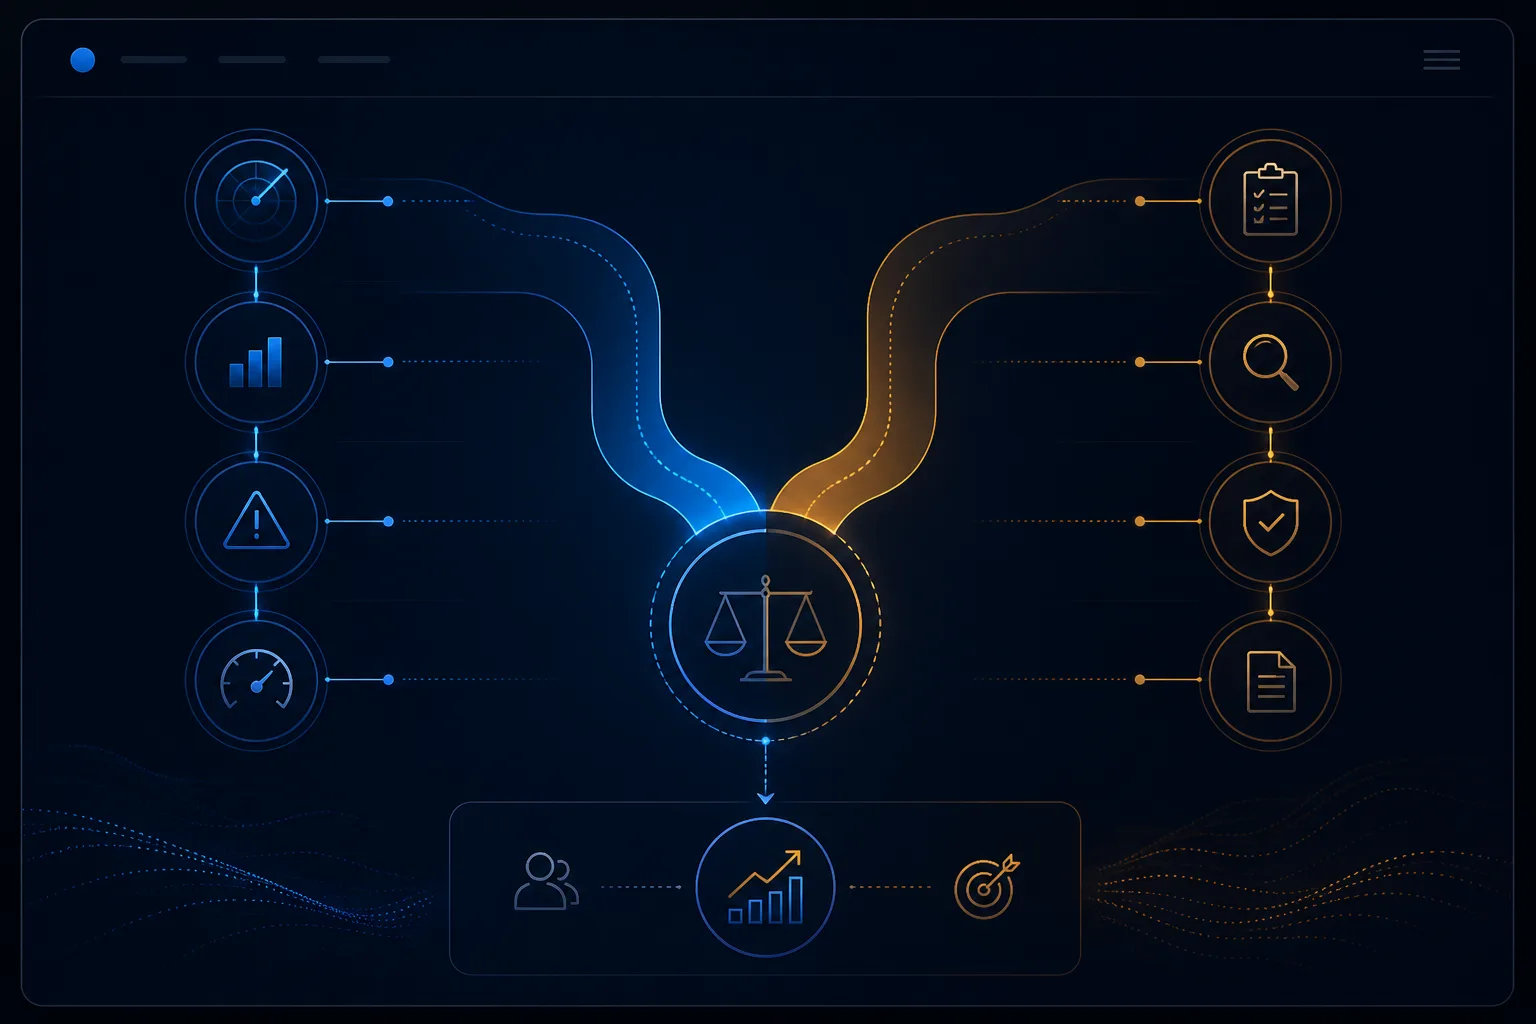
A risk assessment evaluates actual exposure and business impact. A compliance audit tests whether controls align to a framework, standard, or requirement.
Organizations often need both. The mistake is assuming one automatically replaces the other.
In Canada, the Office of the Privacy Commissioner says organizations must report certain breaches that create a real risk of significant harm, and failures to meet breach-reporting obligations can lead to fines of up to $100,000 under PIPEDA. Statistics Canada also reported that 16% of Canadian businesses were impacted by cybersecurity incidents in 2023. Those realities help explain why compliance evidence and real exposure analysis answer different leadership questions.
What a risk assessment does
A risk assessment asks:
- What could materially affect the business?
- How serious is the exposure?
- Which weaknesses matter most right now?
- What should be prioritized first?
It is designed to support judgment, prioritization, and decision-making. It connects technical weakness to business consequence.
That difference matters because leadership usually needs more than a list of controls. It needs to understand which weaknesses are material, which decisions deserve attention first, and where inaction could create operational, financial, or governance consequences.
What a compliance audit does
A compliance audit asks a different set of questions:
- Are required controls present?
- Can they be evidenced appropriately?
- Does the organization align to the chosen framework or obligation?
- Are there gaps between expected controls and what is currently in place?
It is designed to evaluate conformance to a standard or requirement.
An audit can be essential. But it is answering a narrower question. It tests whether expected controls are present and demonstrable. It is not always designed to tell leadership which risk matters most in the real operating environment, or how several weaknesses might combine into a larger business problem.
Why the distinction matters
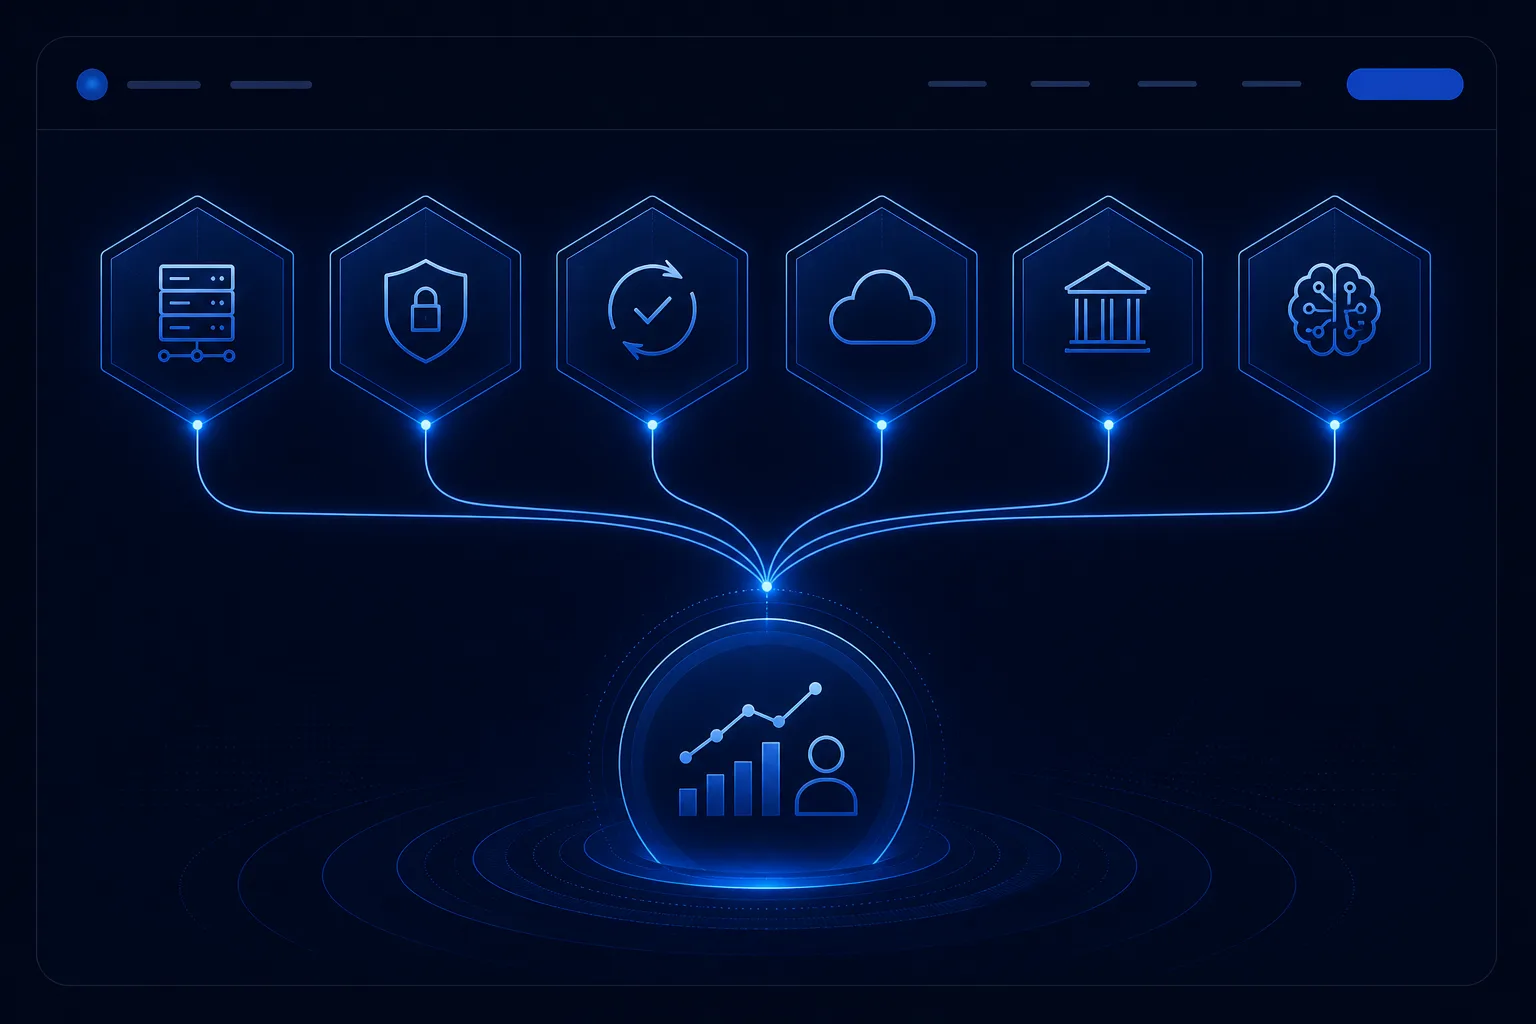
A business can pass parts of a compliance review and still carry meaningful operational risk. It can also understand some of its risks while still being unready for a formal audit.
That is why the two activities should not be treated as interchangeable.
A risk assessment is usually the better starting point when leadership needs to understand actual exposure and where to act first. A compliance audit becomes essential when external obligations, customer requirements, or formal certification expectations are driving the conversation.
This is also why the two efforts can feel different inside the same organization. A compliance program may create structure and evidence. A risk assessment creates prioritization and decision context. Mature organizations often need both, but they should not expect one deliverable to do the full job of the other.
When you need one, the other, or both
Use a risk assessment when the main goal is better visibility, prioritization, and business decision support.
Use a compliance audit when the main goal is proving alignment to a specific framework, standard, or requirement.
Use both when the organization needs to understand real exposure while also preparing to evidence control maturity.
Common mistakes include assuming that a passed audit means the business is low risk, or assuming that an internally understood risk picture is enough when formal evidence will soon be required. Those are different readiness questions, and treating them as interchangeable often delays the right next step.
What the evidence shows
The Office of the Privacy Commissioner of Canada says organizations must report breaches involving personal information when there is a real risk of significant harm, and failures to report can lead to fines of up to $100,000 under PIPEDA.
That matters because compliance obligations can create real consequences even when leadership still lacks a clear understanding of broader exposure.
Statistics Canada reported that 16% of Canadian businesses were impacted by cybersecurity incidents in 2023.
That supports the argument that real exposure analysis matters alongside formal evidence and audit preparation.
Verizon’s 2026 DBIR found that exploitation of vulnerabilities accounted for 31% of breaches, while credential abuse accounted for 13%.
Those findings reinforce why businesses often need risk visibility before they can decide which controls or assurance efforts deserve priority.
The evidence supports a practical conclusion: compliance and risk are related, but they answer different leadership questions and should not be confused with one another.
Frequently asked questions
Final takeaway
NetSentinel belongs on the assessment side of the conversation. It helps leadership understand the wider exposure picture before everything is reduced to audit evidence and framework mapping.
Start with a risk assessment.
If you need a clearer view of what could actually hurt the business before an audit defines the discussion, start with a risk assessment.