What Is IT Governance for Small Business?
Published:
IT governance is the structure that defines how technology decisions are made, who owns what, how change is controlled, and how leadership keeps technology risk aligned with business priorities.
For small and growing businesses, governance is not about creating bureaucracy. It is about making sure important technology decisions are not left to drift, personality, or convenience.
Statistics Canada reported that 16% of Canadian businesses were impacted by cybersecurity incidents in 2023, while total recovery spending rose to about $1.2 billion. The Canadian Centre for Cyber Security also says its baseline controls for small and medium organizations are designed around an 80/20 principle. Those findings reinforce the practical case for governance in smaller organizations: lightweight structure can materially reduce expensive drift.
Why small businesses need it
Many smaller organizations operate with informal technology habits for years. That can work for a while. Over time, though, growth creates more systems, more vendors, more risk, and more consequences when ownership is unclear.
Governance becomes necessary when the business needs better answers to questions like:
- Who owns vendor decisions?
- Who approves change?
- Who is responsible for security, continuity, and policy enforcement?
- How are technology risks escalated to leadership?
- How does the business decide what gets funded first?
Small businesses often avoid governance because they associate it with enterprise bureaucracy. In reality, the need usually appears much earlier and in much simpler ways. A growing business adds systems, vendors, staff, remote access paths, and recurring decisions that can no longer depend entirely on informal habits. Governance is what keeps those decisions from becoming inconsistent, opaque, or overly dependent on one person.
What governance actually covers
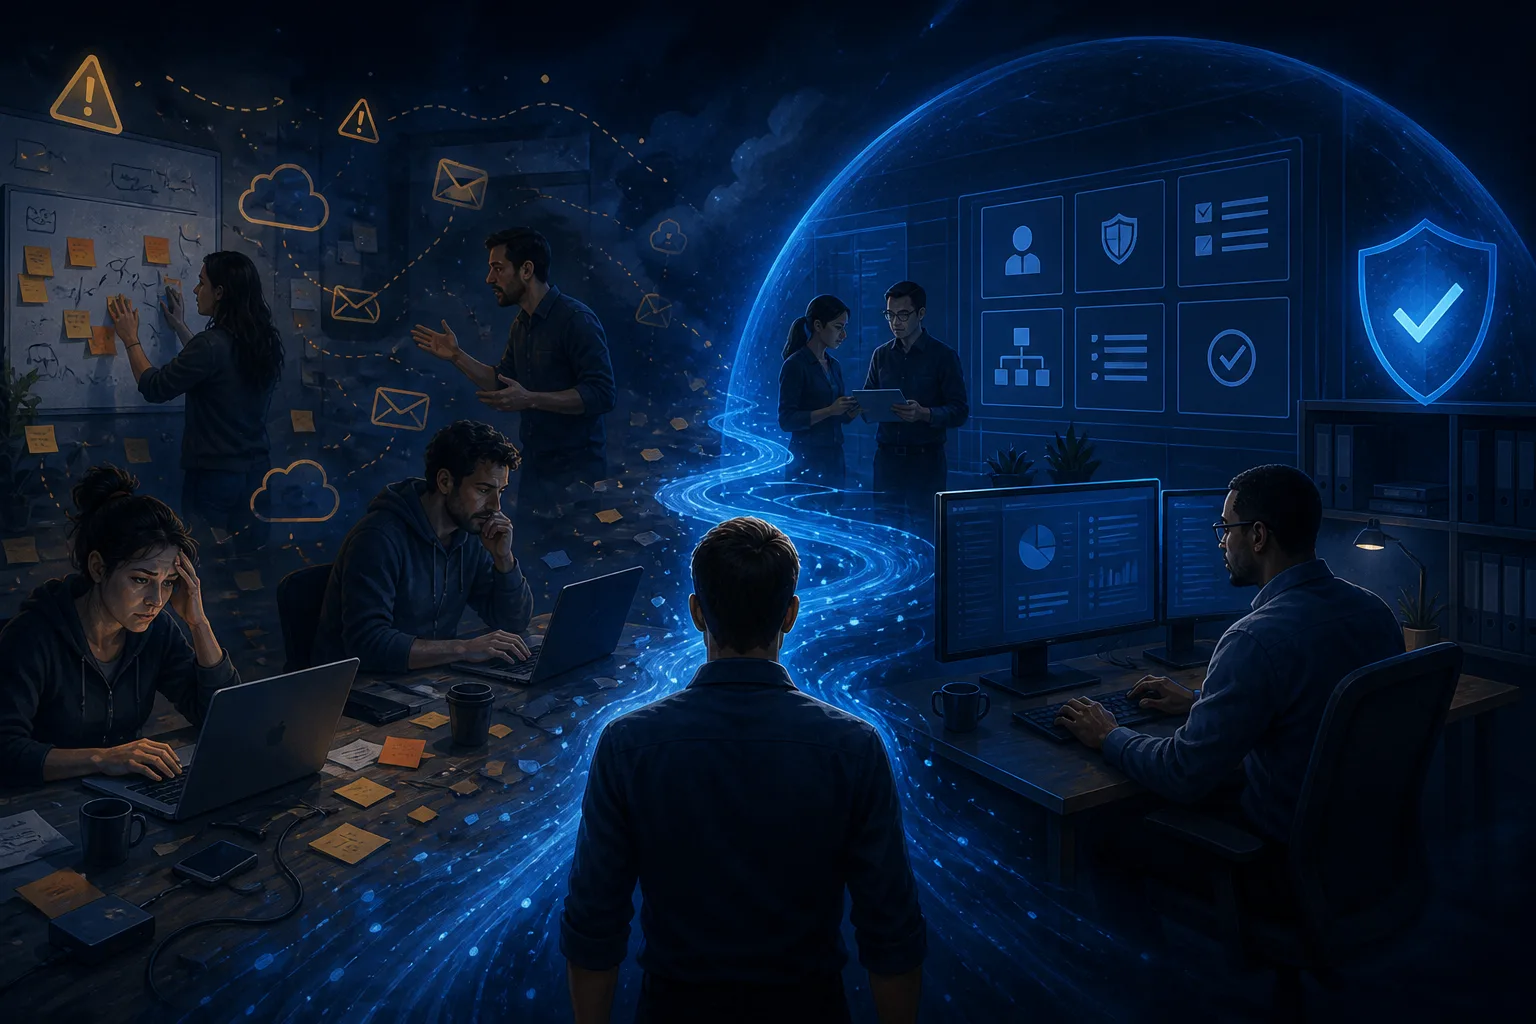
A practical governance model should include:
- policy coverage and accountability
- ownership of systems, vendors, security, and budget
- change-management discipline
- documentation and audit trail quality
- licensing visibility and approval structure
- regular review of risk, priorities, and deferred decisions
Governance is what helps technology management stay deliberate rather than reactive.
It also provides the bridge between leadership and IT. IT may know what is changing operationally. Leadership needs to know how those changes affect ownership, budget, risk tolerance, and accountability. Good governance helps those conversations happen with more structure and less confusion.
Common governance gaps in SMBs
Small businesses often discover governance weakness through:
- undocumented vendor relationships
- unclear responsibility between leadership, IT, and outside providers
- change decisions made without enough approval structure
- policies that exist but do not drive behavior
- repeated delays in addressing known risk because no owner is clearly accountable
These gaps matter because they tend to compound. Weak ownership makes vendor control weaker. Weak vendor control makes change harder to manage. Poorly managed change makes documentation less reliable. Over time, what began as “we are still small enough to handle this informally” becomes a risk pattern that is much harder to unwind.
What good governance looks like in practice
Good governance in a small business does not need to be heavy. It usually looks like:
- clear ownership of systems, vendors, and risk decisions
- lightweight but real approval paths for meaningful change
- policies that match how the business actually works
- visible review dates and named owners
- enough documentation that the business can explain its own decisions later
The goal is not to create procedure for its own sake. The goal is to make important technology decisions more durable, explainable, and easier to govern as the organization grows.
When formal assessment makes sense
A more structured governance assessment is usually worthwhile when:
- leadership wants more accountability around technology decisions
- the business is adding vendors or systems quickly
- audit, insurance, or board questions are becoming more frequent
- known issues keep resurfacing without clear ownership
- the company has outgrown founder-led or purely informal oversight
What the data suggests
Statistics Canada reported that 16% of Canadian businesses were impacted by cybersecurity incidents in 2023, while recovery spending reached about $1.2 billion.
That matters because even smaller organizations face meaningful financial consequences when risk, ownership, and response discipline are weak.
The Canadian Centre for Cyber Security says its baseline controls for small and medium organizations are designed around an 80/20 principle.
That supports the practical governance point for SMBs: lightweight structure can deliver disproportionate benefit without turning the business into a bureaucracy project.
Verizon’s 2025 DBIR said the human element was involved in about 60% of breaches.
That reinforces why governance belongs in the conversation. Many failures involve behavior, process, approvals, or accountability rather than tooling alone.
Taken together, the evidence supports a simple conclusion: small businesses do not need perfect governance. They do need enough structure to stop important technology decisions from drifting.
Frequently asked questions
Final takeaway
Good IT governance improves ownership, decision quality, and business clarity. It helps leadership manage technology as a business system, not just a collection of tools.
Start with an IT Governance Assessment.
If technology is critical to your business but accountability still feels informal, start with an IT Governance Assessment.