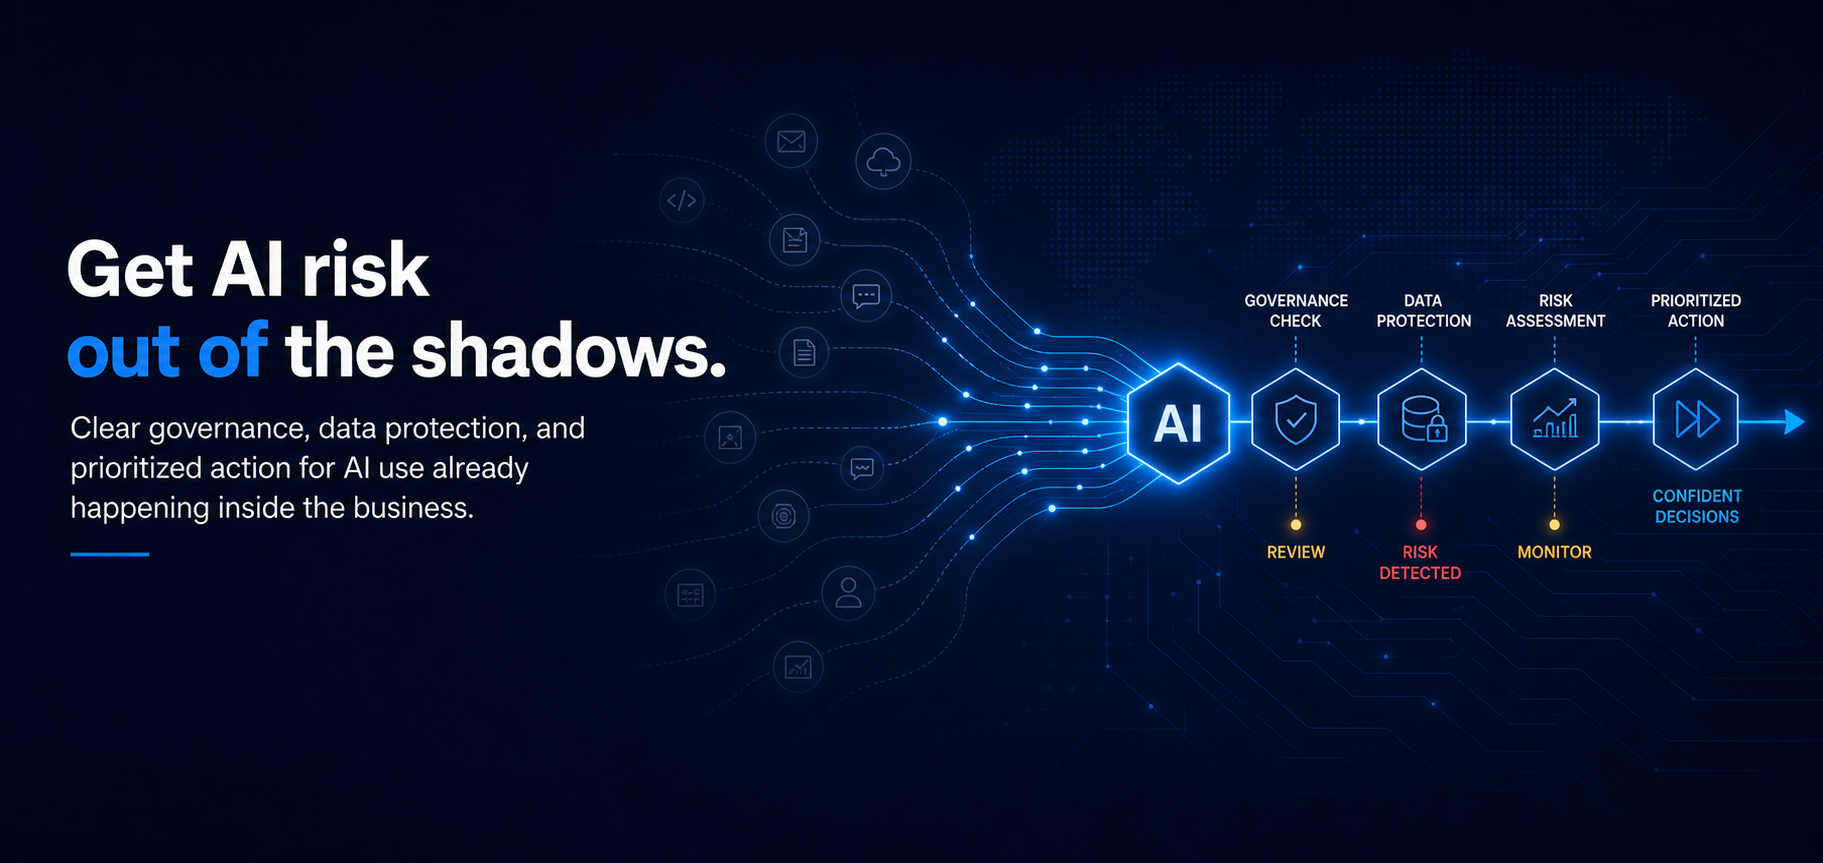
Your Business Is Already Using AI.
Do You Know Where the Risk Is?
Your employees may already be using AI with company data, while leadership has no policy, inventory, ownership, or visibility.
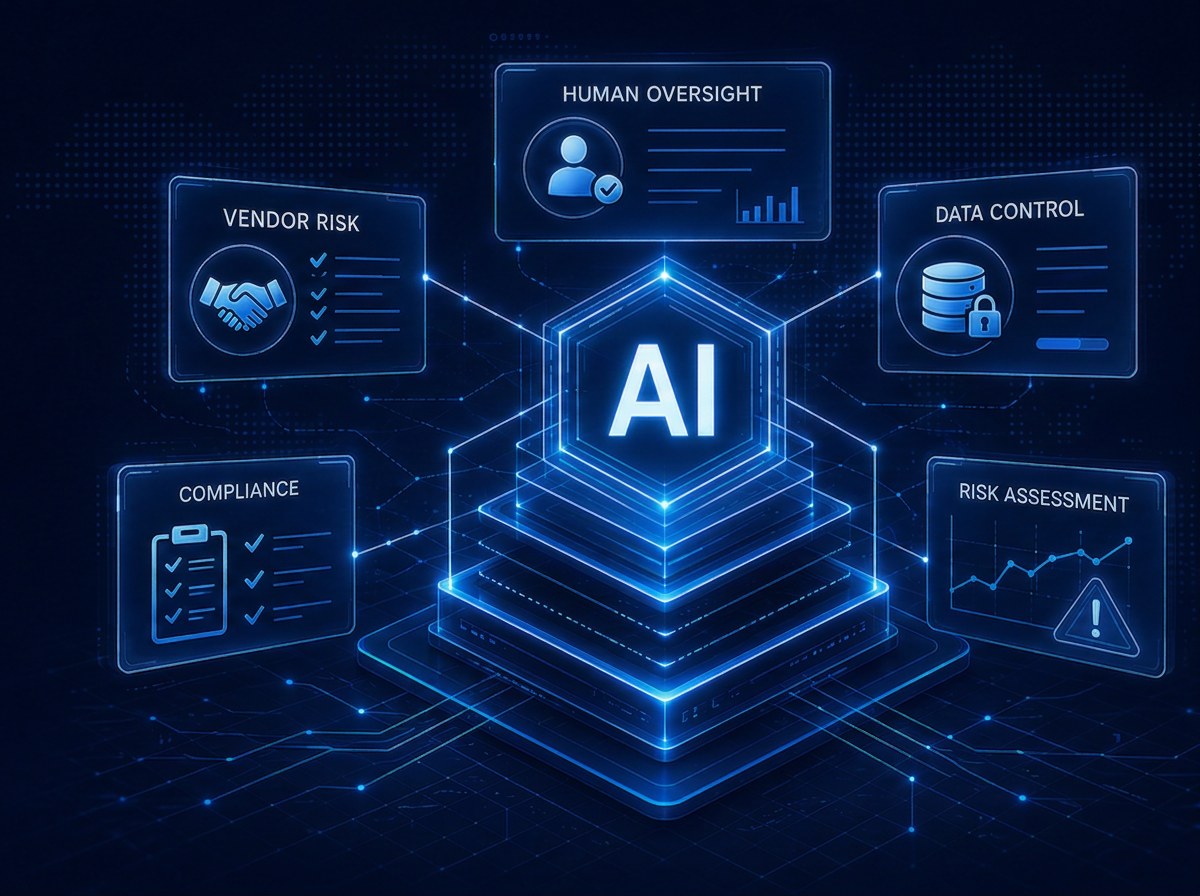
NetSentinel assesses AI governance, data exposure, vendor risk, infrastructure readiness, and responsible adoption—so leadership can understand what is happening, where the gaps are, and what needs to happen next.
Built for executives, SMB owners, consultants, and IT leaders
Map AI use
Understand where AI is already in play.
Set guardrails
Define safe use and policy controls.
Protect data
Reduce leakage and exposure risk.
Measure readiness
Assess governance and operational maturity.
Report clearly
Give leadership decision-ready visibility.
AI adoption often starts before governance does
Employees experiment with public AI tools. Departments buy their own platforms. Sensitive information gets entered into systems leadership has never reviewed. Policies arrive late—after usage has already spread.
NetSentinel gives leadership a clear view of AI use, exposure, ownership, readiness, and risk.
- Shadow AI is already happening
- Policies are often missing or incomplete
- Data may be entering unapproved tools
- Ownership and accountability are unclear
- Leadership lacks visibility
- Risk grows before governance catches up
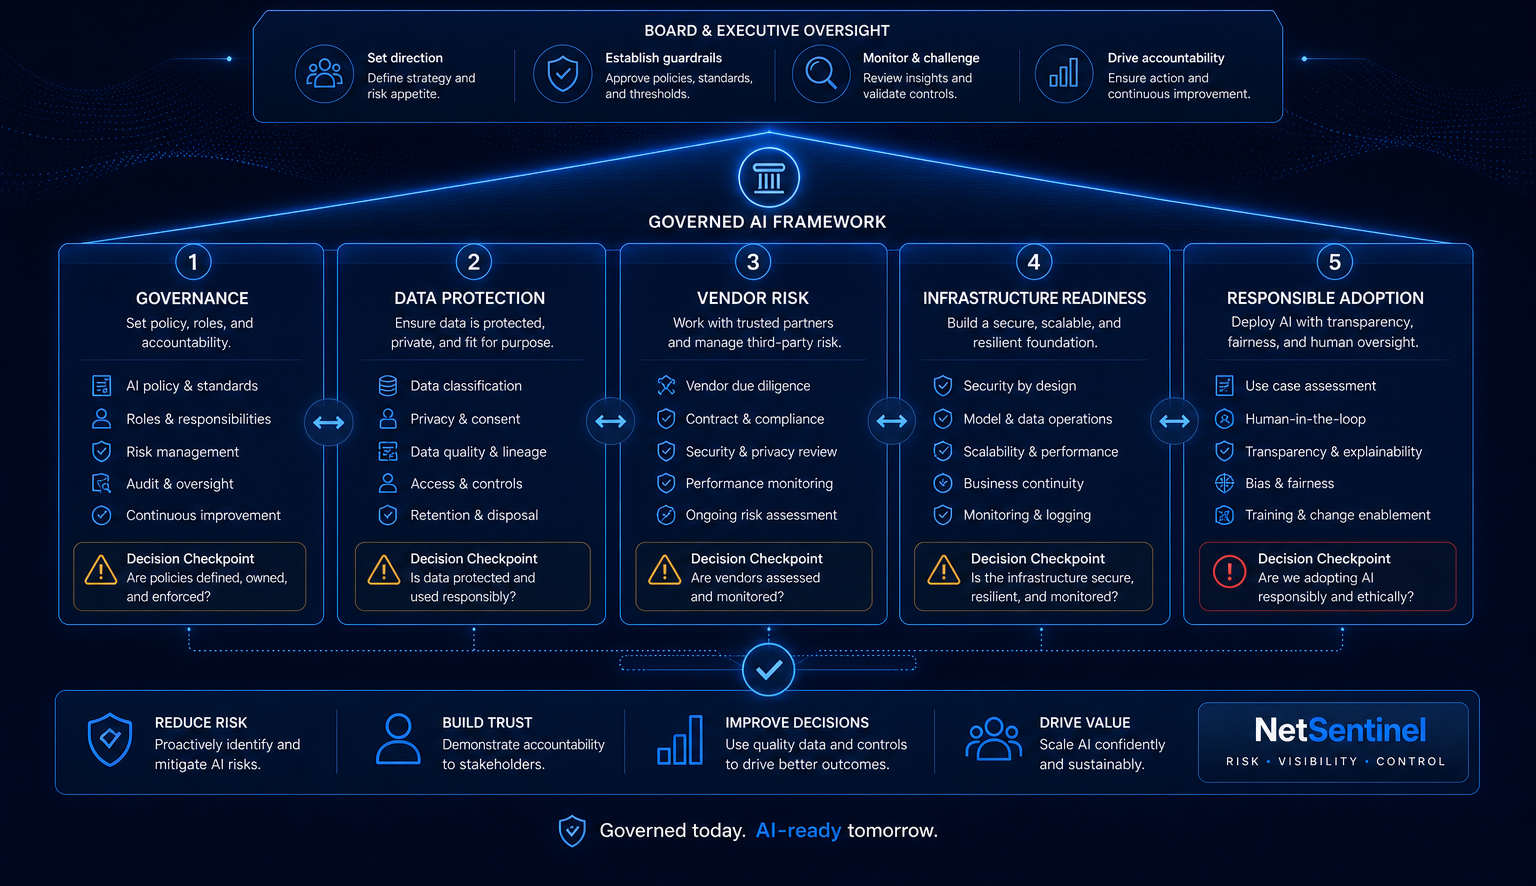
What We Assess
Seven connected areas of AI readiness and governance — evaluated together, not in isolation.
AI Usage Visibility
Assess where AI tools are being used across teams and workflows.
Governance & Policy
Evaluate acceptable-use policies, approvals, ownership, and oversight.
Data Exposure
Identify where business, client, or sensitive data may be entering AI tools.
Vendor Risk
Assess third-party AI platforms, dependencies, and concentration risk.
Operational Readiness
Measure whether AI use is aligned with process, accountability, and control.
Infrastructure & Identity Readiness
Review supporting systems, access controls, permissions, and integration maturity.
Reporting & Leadership Oversight
Turn technical complexity into executive clarity and board-ready reporting.
See AI risk the way leadership needs to see it
NetSentinel translates AI exposure and governance maturity into a clear executive score—so leaders can understand where risk sits, which areas need attention, and what to prioritize first.
- Surface hidden AI exposure
- Identify governance gaps
- Prioritize practical next steps
- Support leadership decisions
Overall NetSentinel AI Score
- AI Usage Visibility78
- Governance & Policy61
- Data Exposure69
- Vendor Risk66
- Operational Readiness74
- Infrastructure & Identity Readiness70
- Reporting & Leadership Oversight71
Illustrative example. Your score reflects your own assessment responses.
What leadership sees after the assessment
A single board-ready view of AI readiness: an overall score, maturity level, area-by-area status, priority actions, and a plain-language executive interpretation.
NetSentinel executive preview
AI Readiness Dashboard
Overall readiness
Developing
Level 3 of 5 — adoption is underway, governance is behind.
Overall AI readiness score 72 out of 100, maturity level Developing.- Unsanctioned AI tools in use7
- Approved AI tools4
- Governance policies in place1 of 5
Readiness by area
AI Usage Visibility
Most AI tool usage is now identified
Governance & Policy
No approved AI use policy
Data Exposure
Classification partially defined
Vendor Risk
AI clauses missing from contracts
Operational Readiness
Ownership defined for most workflows
Infrastructure & Identity Readiness
Access controls extend to most AI tools
Reporting & Leadership Oversight
Reporting is periodic, not yet routine
Priority actions
- 1Publish an approved AI use policy and name an accountable owner
- 2Inventory unsanctioned AI tools and the data being entered into them
- 3Add AI and data-handling clauses to vendor contracts at renewal
Executive interpretation
AI is already embedded in day-to-day work, but oversight has not kept pace. AI usage visibility and operational readiness are the strongest domains; governance & policy and vendor risk are the weakest. The fastest risk reduction comes from formal ownership and a published policy — not from slowing adoption. The overall score weights the seven domains by executive risk impact; it is not a simple average.
Illustrative example only. Scores, levels, and actions reflect your own assessment responses.
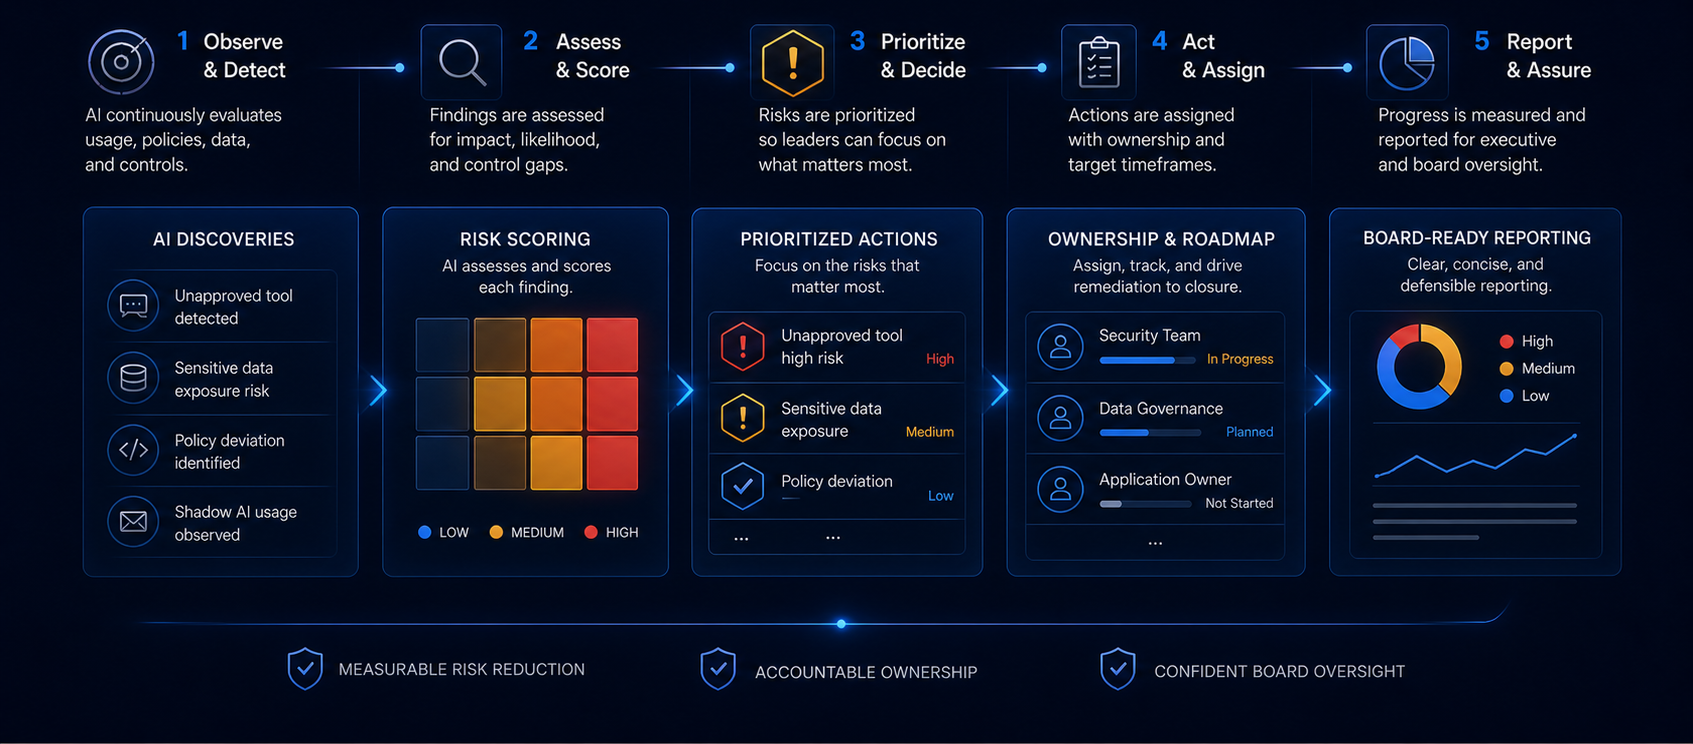
From AI findings to prioritized, reportable action
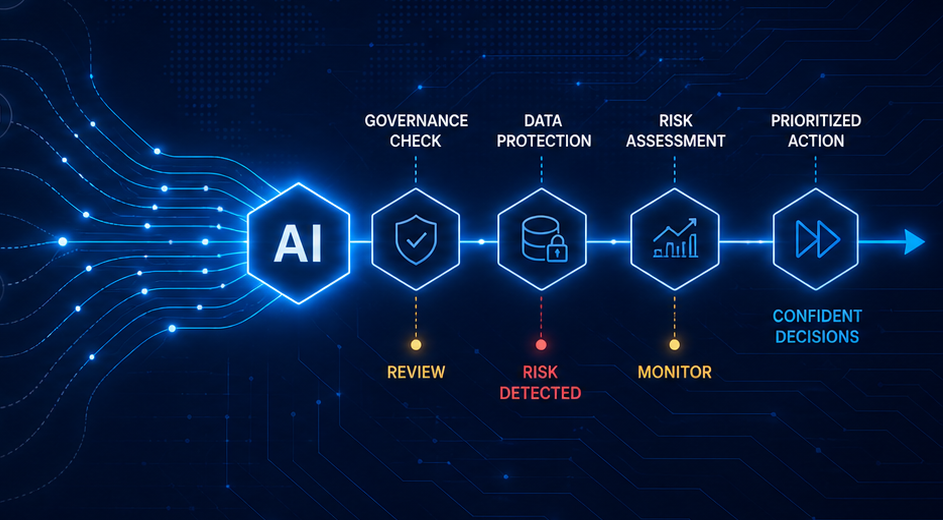
Assessment findings are scored for impact and control gaps, prioritized so leadership can focus on what matters most, assigned to owners with target timeframes, and reported in a format the board can act on.
Bring AI complexity into view — before it becomes business risk
Assess AI tool usage, governance maturity, data exposure, vendor dependency, and operational readiness before fragmented adoption creates larger business problems.
- Business Use Cases
- AI Applications & Tools
- Data & Knowledge Sources
- Identity & Access
- Integrations & Automation
- Infrastructure & Platforms
- Policy & Governance Foundation
- Asset visibility
Identify tools, workflows, and dependencies.
- Policy controls
Align AI use with business rules and approvals.
- Data exposure
Identify where sensitive information may be at risk.
- Vendor risk
Evaluate third-party dependencies and concentration.
- Operational readiness
Measure process maturity and ownership.
- Incident readiness
Understand how issues are escalated, owned, and managed.
Key AI risk areas leadership should understand
Shadow AI
Unapproved use of AI tools across the business.
Data Leakage
Sensitive information entering tools without oversight.
Governance Gap
AI adoption outpacing policy, ownership, and control.
Vendor Dependency
Concentrated reliance on external AI platforms.
Operational Readiness
Whether workflows, people, and controls are prepared.
Accountability
Clear ownership for AI decisions, approvals, and risk.
Move beyond AI enthusiasm to AI control
NetSentinel does not treat AI as a buzzword. It treats AI as an executive risk, governance, and readiness issue.
Our assessment helps leadership understand
- Where AI is being used
- What data may be exposed
- Where policy is missing
- Which vendors create concentration risk
- How ready the business really is
- What needs to happen next
- Executive-level visibility
- Structured, board-ready reporting
- Practical, business-first risk framing
- Clear priorities and next steps
Frequently asked questions.
NetSentinel provides structured technology-risk visibility and decision support. It does not perform AI model auditing or penetration testing, certify compliance, monitor environments, or replace specialist legal, regulatory, cybersecurity, or professional advice.
Bring AI risk into view before it becomes harder to control
Understand how AI is being used, where the gaps are, and what leadership needs to do next.
Questions first? Contact us.