Microsoft 365 Security Assessment Guide
Published:
A Microsoft 365 security assessment should do more than confirm whether recommended settings are turned on. It should show how identity, access, collaboration, data protection, device trust, and recovery controls work together across the tenant, where real exposure paths exist, and which gaps create material business risk.
For many organizations, Microsoft 365 is no longer just email and file storage. It is the operational control plane for identity, collaboration, endpoint trust, third-party SaaS access, and increasingly AI through Copilot.
Microsoft said in its 2025 Digital Defense Report that identity-based attacks rose 32% in the first half of 2025 and that more than 97% of those attacks were large-scale password-based attempts. Microsoft Research has also found that multifactor authentication can prevent over 99.2% of account compromise attacks. In a tenant that now acts as the identity and collaboration control plane, those findings reinforce why identity and privilege design deserve executive attention.
Why Microsoft 365 deserves a serious review
A useful assessment is not a screenshot of Secure Score and it is not a generic hardening checklist.
It is a review of whether the tenant’s control design is strong enough for the way the business actually works. That means looking beyond individual settings and asking harder questions:
- Are privileged roles tightly controlled?
- Are sharing defaults appropriate?
- Are risky access paths visible?
- Is the environment governed well enough to support growth and AI expansion?
- Would recovery actually work under pressure?
Those questions matter because Microsoft 365 is often both highly visible and poorly understood. Staff rely on it constantly, leadership assumes it is central, and IT keeps adjusting it as the business changes. Over time, permissions, group memberships, sharing patterns, and app integrations can evolve into a much broader risk surface than the tenant’s original design ever anticipated.
What a strong assessment should cover
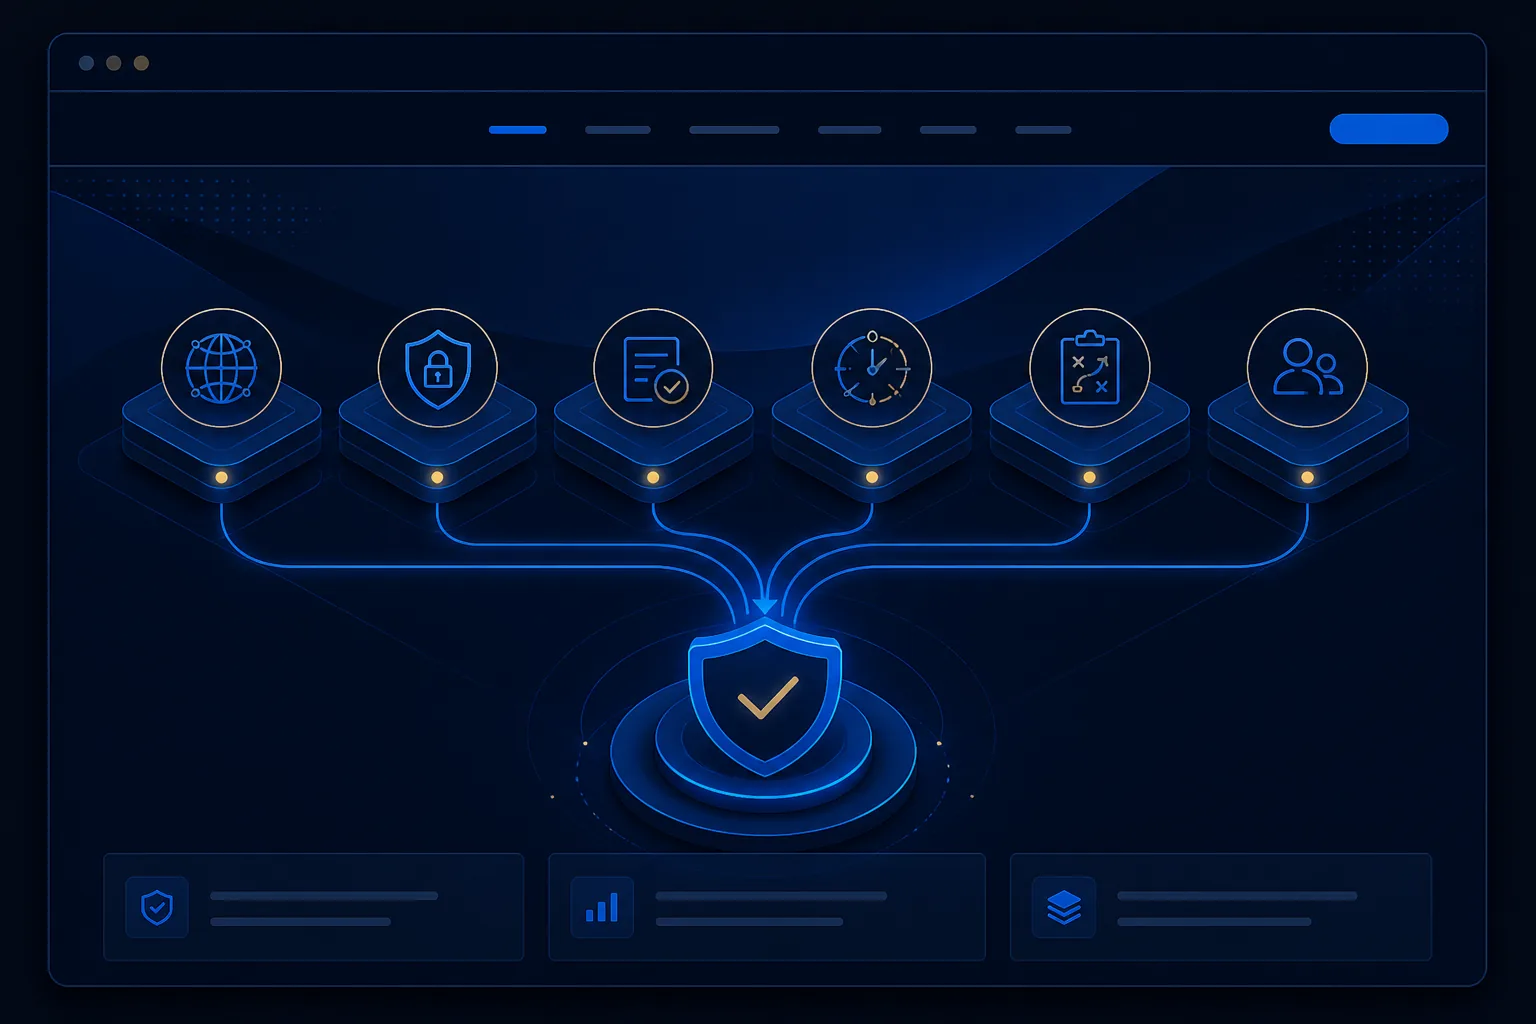
A credible Microsoft 365 review should examine:
- identity and privileged-access design
- authentication strength and conditional-access maturity
- device trust and endpoint dependency
- collaboration, guest access, and external sharing exposure
- email security and mailbox control gaps
- data protection, retention, and governance readiness
- logging, detection, and response visibility
- backup, recovery, and operational resilience
- third-party app consent and OAuth exposure
- licensing constraints that affect control design
The goal is not to produce an admin checklist with more screenshots. It is to understand how the tenant behaves as a real operating environment. That includes whether identities are trusted too broadly, whether collaboration controls reflect current reality, whether administrative power is too concentrated, and whether the business could explain or recover from a serious control failure.
Why this matters for leadership
In many SMB environments, Microsoft 365 has become the front door to the business. Weak identity design, permissive sharing, or under-governed collaboration can affect email, documents, meetings, admin access, and AI-enabled search or summarization at the same time.
That makes Microsoft 365 risk a business issue, not just an admin issue.
Leadership does not need more technical noise. It needs clarity on where control weakness could turn into disruption, exposure, governance failure, or poor recovery performance.
That is why a serious assessment should connect technical conditions to executive decisions. Which issues deserve funding first? Where is oversharing likely to create confidentiality exposure? How much administrative privilege is too much for the current operating model? What would leadership need to explain if a customer, insurer, or board member asked how the environment is governed?
Common signs the environment needs review
A serious assessment is especially valuable when:
- too many people hold administrative privilege
- Secure Score is being treated as the main proof of security
- external sharing has expanded over time
- Copilot or other AI features are being considered
- app consent and SaaS integrations are lightly governed
- restore confidence is weaker than the backup story suggests
Other warning signs include inherited permissions that no one fully trusts, years of collaboration growth without clear ownership, and a general reliance on the idea that “Microsoft probably covers most of that.” A Microsoft 365 tenant can be busy, productive, and still materially under-governed.
What strong Microsoft 365 maturity looks like
Strong maturity does not mean the tenant is perfect. It means the organization can explain its identity model, privileged-access approach, sharing standards, app-approval discipline, and recovery assumptions clearly enough that business leaders can make defensible decisions about remaining risk.
Weak maturity usually looks more familiar: too many admins, broad legacy groups, unclear guest access standards, disconnected data-governance practices, and confidence that depends too heavily on Secure Score or default vendor messaging. An assessment helps distinguish between visible activity and real control quality.
What current evidence shows
Microsoft said in its 2025 Digital Defense Report that identity-based attacks rose 32% in the first half of 2025.
That matters because Microsoft 365 often acts as the identity and collaboration control plane for the business.
Microsoft also reported that more than 97% of those identity-based attacks were large-scale password-based attempts.
This reinforces why weak authentication and over-broad access design can create meaningful tenant risk even when the environment looks productive and familiar.
Microsoft Research found that multifactor authentication can prevent over 99.2% of account compromise attacks.
That is strong support for treating identity maturity as a first-order Microsoft 365 security issue.
These facts matter because Microsoft 365 risk is usually less about one dramatic setting and more about whether identity, privilege, sharing, governance, and recovery assumptions are strong enough for the role the tenant now plays in the business.
Frequently asked questions
Final takeaway
A Microsoft 365 tenant can look mature on the surface while still carrying material exposure through identity design, collaboration settings, over-privileged access, or weak governance.
Related reading: Technology Risk Assessment, Cybersecurity Risk Assessment Services, and AI Readiness Assessment Services.
Test control design before the stakes rise
If Microsoft 365 has become the operational control plane for your business, start with an assessment that tests control design, exposure paths, and recovery readiness before growth or AI adoption raises the stakes.